

In another lesson, I explained the different EIGRP packets and their function. In this lesson, we’ll take a close look at the EIGRP neighbor adjacency to see what exactly happens when EIGRP routers become neighbors. This is what happens when you enable EIGRP on two routers:
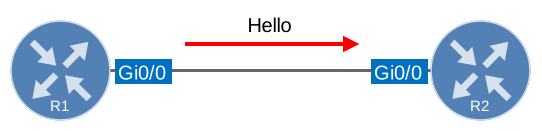
We have two routers called R1 and R2, and they are configured for EIGRP. As soon as we enable it for the interface, they will start sending hello packets. In this example, R1 is the first router to send a hello packet.
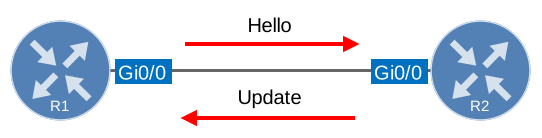
As soon as R2 receives the hello packet from R1 it will respond by sending an update packet with the initialization bit set, so we know this is the “initialization process.” This first update is empty. It tells R1 to send its routes, and R2 can’t send any other update packets until R1 has acknowledged it. At this moment, there is still no neighbor adjacency until R2 has sent a hello packet to R1.
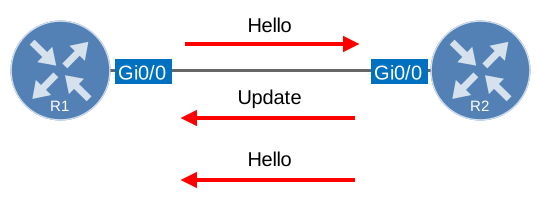
R1 is, of course, not the only one sending hello packets. As soon as R2 sends a hello packet to R1 we can continue to set up a neighbor adjacency.
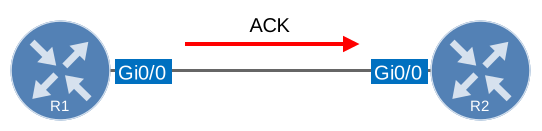
After both routers have exchanged hello packets, we will establish the neighbor adjacency. R1 will send an ACK to let R2 know he received the update packet. R2 can now send update packets that contain all the routing information that it has in its routing table. The only routes not sent on this interface are the ones that R2 learned on this interface because of split horizon. R1 saves this information in the EIGRP topology table.
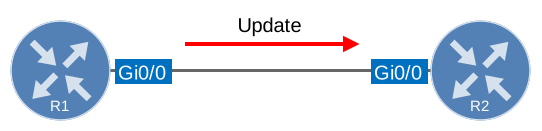
R2 is anxious to receive routing information as well, so R1 will send update packets to R2, which will save this information in its EIGRP topology table.
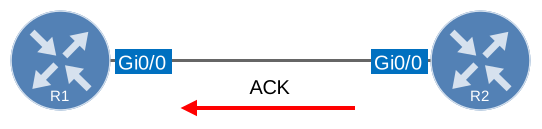
After receiving the update packets, R2 will send an ACK back to R1 to let him know everything is ok.
Configuration
Want to see what this looks like on a real router? Let’s use the following topology and see what happens:
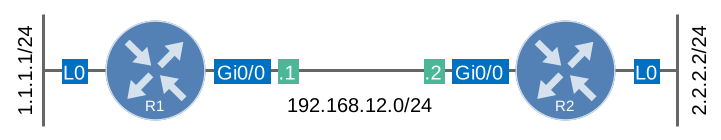
This is the topology I’m going to use to configure EIGRP. R1 and R2 are IOSv routers running Cisco IOS 15.9(3)M9. My goal is to have full connectivity, and here are the configurations:
R1(config)#router eigrp 1
R1(config-router)#no auto-summary
R1(config-router)#network 1.1.1.0 0.0.0.255
R1(config-router)#network 192.168.12.0
R1(config-router)#exitR2(config)#router eigrp 1
R2(config-router)#no auto-summary
R2(config-router)#network 2.2.2.0 0.0.0.255
R2(config-router)#network 192.168.12.0
R2(config-router)#exitLet’s break this one down. Router eigrp 1 will start up EIGRP using AS (autonomous system) number 1. This number has to match on both routers, or we won’t become EIGRP neighbors.
No auto-summary is needed because, on older IOS versions, EIGRP summarizes networks to their classful network boundary when it advertises them into another major network. In this case, that means that 1.1.1.0/24 and 2.2.2.0/24 will be advertised as 1.0.0.0/8 and 2.0.0.0/8. Disabling auto-summary will ensure EIGRP advertises the /24 subnets. EIGRP always includes the subnet mask in its updates, even with auto-summary enabled.
Network 1.1.1.0 0.0.0.255 means I’m advertising the 1.1.1.0 network with wildcard 0.0.0.255. If I don’t specify the wildcard, you’ll find “network 1.0.0.0” in your configuration. Does it matter? Yes and no. The same thing applies to “network 2.2.2.0 /24”. It will work but it also means that every interface that falls within the 1.0.0.0/8 or 2.0.0.0/8 range is going to run EIGRP. Network 192.168.12.0 without a wildcard mask is fine since I’m using a /24 on this interface which is Class C.
If you are working on a lab and are lazy, you can also type in network 0.0.0.0, which will activate EIGRP on all of your interfaces.
Let’s do a debug on R2 to see what is going on:
R2#debug eigrp packets ?
  <1-99>       Access list
  <1300-1999>  Access list (expanded range)
  SIAquery     EIGRP SIA-Query packets
  SIAreply     EIGRP SIA-Reply packets
  ack          EIGRP ack packets
  all          Display all EIGRP packets
  hello        EIGRP hello packets
  query        EIGRP query packets
  reply        EIGRP reply packets
  request      EIGRP request packets
  retry        EIGRP retransmissions
  stub         EIGRP stub packets
  terse        Display all EIGRP packets except Hellos
  update       EIGRP update packets
  <cr>         <cr>
As you can see, we have many debug options for EIGRP. I want to see the hello packets:
R2#debug eigrp packets hello
    (HELLO)
EIGRP Packet debugging is on
R2#
EIGRP: Received HELLO on Gi0/0 - paklen 20 nbr 192.168.12.1
AS 1, Flags 0x0:(NULL), Seq 0/0 interfaceQ 0/0This is looking good. It seems we have received a hello packet from R1. R2 sends a hello packet to R1 as well:
R2#
EIGRP: Sending HELLO on Gi0/0 - paklen 30
  AS 1, Flags 0x0:(NULL), Seq 0/0 interfaceQ 0/0 iidbQ un/rely 0/0
A little later, we have an EIGRP neighbor adjacency:
R1#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.2 (GigabitEthernet0/0) is up: new adjacency
R2#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.1 (GigabitEthernet0/0) is up: new adjacencyIf you look at the EIGRP interfaces of R2, you can see something interesting:
R2#show ip eigrp interfaces
EIGRP-IPv4 Interfaces for AS(1)
                              Xmit Queue   PeerQ        Mean   Pacing Time   Multicast    Pending
Interface              Peers  Un/Reliable  Un/Reliable  SRTT   Un/Reliable   Flow Timer   Routes
Lo0                      0        0/0       0/0           0       0/0            0           0
Gi0/0                    1        0/0       0/0          13       0/0           60           0
R2 runs EIGRP on its loopback interface too. It won’t find any EIGRP neighbors there, though.
This behavior is normal because the network command does two things:
- Run EIGRP on the interface that falls within the network command range, so it can send EIGRP packets and form neighbors there.
- Advertise the network that is configured on the interface in EIGRP.
So what do you have to do when you want to advertise a network without sending EIGRP packets on the interface and forming EIGRP neighbors?
You use the passive-interface command:
R2(config)#router eigrp 1
R2(config-router)#passive-interface loopback 0
The loopback interface is gone from the EIGRP interfaces:
R2#show ip eigrp interfaces
EIGRP-IPv4 Interfaces for AS(1)
                              Xmit Queue   PeerQ        Mean   Pacing Time   Multicast    Pending
Interface              Peers  Un/Reliable  Un/Reliable  SRTT   Un/Reliable   Flow Timer   Routes
Gi0/0                    1        0/0       0/0          13       0/0           60           0
This will advertise the 2.2.2.0/24 network on R2’s loopback 0 interface without sending EIGRP packets to the loopback. If you have to configure an ISP router with 50+ interfaces, you probably don’t want to type in this command on each of those interfaces. You can also configure passive-interface default and only activate the interfaces you want to run EIGRP on. Here is an example:
R2(config)#router eigrp 1
R2(config-router)#passive-interface default
R2(config-router)#no passive-interface gigabitEthernet 0/0
Let’s look at a debug of some EIGRP update packets. First, we enable the debug:
R2#debug eigrp packets update
    (UPDATE)
EIGRP Packet debugging is on
And now we clear the neighbor adjacency:
R1#clear ip eigrp neighborsThis is what you’ll see on R1:
R1#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.2 (GigabitEthernet0/0) is down: manually cleared
R1 is the router where we cleared the neighbor adjacency, so it logs manually cleared. A short while later, we reestablish the neighbor adjacency:
R1#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.2 (GigabitEthernet0/0) is up: new adjacency
R1 is back in business, and our EIGRP neighbor adjacency has been re-established. Here’s what R2 shows:
R2#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.1 (GigabitEthernet0/0) is down: Interface PEER-TERMINATION received
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.1 (GigabitEthernet0/0) is up: new adjacency
EIGRP: Enqueueing UPDATE on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0 iidbQ un/rely 0/1 peerQ un/rely 0/0
EIGRP: Received UPDATE on Gi0/0 - paklen 0 nbr 192.168.12.1
  AS 1, Flags 0x1:(INIT), Seq 7/0 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
EIGRP: Sending UPDATE on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0
  AS 1, Flags 0x1:(INIT), Seq 10/7 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
EIGRP: Received UPDATE on Gi0/0 - paklen 44 nbr 192.168.12.1
  AS 1, Flags 0x8:(EOT), Seq 8/0 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
EIGRP: Enqueueing UPDATE on Gi0/0 - paklen 0 tid 0 iidbQ un/rely 0/1 serno 1-2
EIGRP: Sending UPDATE on Gi0/0 - paklen 44 tid 0
  AS 1, Flags 0x8:(EOT), Seq 11/0 interfaceQ 0/0 iidbQ un/rely 0/0 serno 1-2
EIGRP: Received UPDATE on Gi0/0 - paklen 44 nbr 192.168.12.1
  AS 1, Flags 0x8:(EOT), Seq 8/11 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/0
EIGRP: Received UPDATE on Gi0/0 - paklen 44 nbr 192.168.12.1
  AS 1, Flags 0x0:(NULL), Seq 9/0 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/0
EIGRP: Enqueueing UPDATE on Gi0/0 - paklen 0 tid 0 iidbQ un/rely 0/1 serno 6-6
EIGRP: Sending UPDATE on Gi0/0 - paklen 44 tid 0
  AS 1, Flags 0x0:(NULL), Seq 12/0 interfaceQ 1/0 iidbQ un/rely 0/0 serno 6-6
R2 logs Interface PEER-TERMINATION received. You can see that EIGRP neighbors tell each other when they are clearing the neighbor adjacency. R1 does this with a hello packet that has all K values set to 255.
Once we have a neighbor adjacency, we’ll exchange UPDATE packets. Above, you can see R2 is putting an update packet in its queue for R1. R2 is also receiving an update packet from R1 and afterward sending its own update packet. These two have the INIT flag set (Flags 0x1:(INIT)) and a packet length of 0, so they are empty. The routes follow in the updates with the EOT flag (Flags 0x8:(EOT)). You’ll see a couple of update packets flying back and forth.
We can also check out some acknowledgments by debugging ack packets:
R2#debug eigrp packets ack
    (ACK)
EIGRP Packet debugging is on
Let’s reset the neighbor adjacency again:
R1#clear ip eigrp neighborsHere’s what you’ll get:
R2#
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.1 (GigabitEthernet0/0) is down: Interface PEER-TERMINATION received
%DUAL-5-NBRCHANGE: EIGRP-IPv4 1: Neighbor 192.168.12.1 (GigabitEthernet0/0) is up: new adjacency
EIGRP: Received ACK on Gi0/0 - paklen 0 nbr 192.168.12.1
  AS 1, Flags 0x0:(NULL), Seq 0/13 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
EIGRP: Received ACK on Gi0/0 - paklen 0 nbr 192.168.12.1
  AS 1, Flags 0x0:(NULL), Seq 0/14 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
EIGRP: Enqueueing ACK on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0
  Ack seq 11 iidbQ un/rely 0/0 peerQ un/rely 1/0
EIGRP: Sending ACK on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0
  AS 1, Flags 0x0:(NULL), Seq 0/11 interfaceQ 1/0 iidbQ un/rely 0/0 peerQ un/rely 1/0
EIGRP: Enqueueing ACK on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0
  Ack seq 12 iidbQ un/rely 0/1 peerQ un/rely 1/0
EIGRP: Sending ACK on Gi0/0 - paklen 0 nbr 192.168.12.1 tid 0
  AS 1, Flags 0x0:(NULL), Seq 0/12 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 1/1
EIGRP: Received ACK on Gi0/0 - paklen 0 nbr 192.168.12.1
  AS 1, Flags 0x0:(NULL), Seq 0/15 interfaceQ 0/0 iidbQ un/rely 0/0 peerQ un/rely 0/1
These are the ack packets in response to some of the update packets. If you want to see the whole process, we can combine some debugging:
R2#debug eigrp packets
    (UPDATE, REQUEST, QUERY, REPLY, HELLO, UNKNOWN, PROBE, ACK, STUB, SIAQUERY, SIAREPLY)
EIGRP Packet debugging is on
This is how you enable debugging for all EIGRP packets. Reset the neighbor adjacency once more:
R1#clear ip eigrp neighborsAnd you’ll see plenty of debugging information:
Hi ,
I did not understand this
“As soon as router John receives the hello packet from Jack it will respond by sending update packets that contain all the routing information that it has in its routing table. The only routes that are not sent on this interface are the one that John learned on this interface because of split-horizon”
router will send an UPDATE without forming a neighbor relationship??
Jack has not shared any update to john, then how john will come to know the prefix of jack so there is no point of split horizon here.
please correct me if am wrong…
Hi Praveen,
You would expect that the routers would send 1 hello, receive 1 hello and then exchange routing information but it’s not the way it works with EIGRP. Once an EIGRP-enabled router receives a hello packet, it will send an update packet. A good way to see this in action is to configure EIGRP on two routers and then use an inbound access-list on one router that filters traffic destined for 224.0.0.10. If you do this, one router will filter all hello packets and you’ll see that its neighbor will still send update packets.
Forming the neighborship
... Continue reading in our forumHi Rene,
On below config advertisement
John(config)#router eigrp 1
John(config-router)#no auto-summary
John(config-router)#network 2.2.2.0 0.0.0.255
John(config-router)#network 192.168.12.0
John(config-router)#exit
if i add below config on it
John(config)#router eigrp 1
John(config-router)#passive-interface loopback 0
That means traffic for network 2.2.2.0/24 and 192.168.12.0 won’t pass on interface loop back 0 ?
Hi Dani,
If you use the passive-interface command then it will no longer send EIGRP hello packets on that interface, that’s it. Here’s an example:
https://networklessons.com/eig...passive-interface
Rene
Thank You very much Rene for a nice elaboration. kindly share also the detail on how redistribute and connected command work on EIGRP.