Lesson Contents
By default the Cisco ASA firewall has a self signed certificate that is regenerated every time you reboot it. This can be an issue when you are using SSL VPN as the web browser of your user will give a warning every time it sees an untrusted certificate. In another lesson where I explained how to configure AnyConnect remote access VPN (Cisco has since renamed the AnyConnect client to Cisco Secure Client), you can see these errors when the remote users connect to the ASA. To fix this problem we have two options:
- Purchase and install an SSL certificate on the ASA from a trusted CA.
- Generate a self signed SSL certificate on the ASA and export it to your user’s computer.
The first option is the best one, you buy an SSL certificate from a provider like Verisign, Entrust, Godaddy, etc. and install it on the ASA. Web browsers have a lot of pre-installed root CA certificates from these providers so when you get an SSL certificate from them, your browser will show them as trusted. This is great because you don’t have to do anything on the user’s computer.
If you don’t want to buy an SSL certificate then we can use the second option. We will generate an SSL certificate on the ASA and self-sign it. This certificate is permanent so it doesn’t disappear when you reboot the ASA, the problem however is that you have to export and import this certificate on each of your remote users’ computers.
That’s what we will do in this lesson…we will generate the SSL certificate, self-sign it and then export and import it on a remote user’s computer. This is the topology I will use:
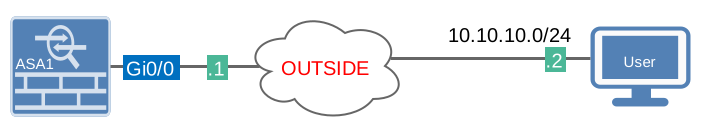
The ASA is connected to a remote user on its outside interface. I’m using an ASAv running ASA software version 9.24(1). The user’s computer will run Windows 7. Let’s get started shall we?
ASA Configuration
There are a number of requirements when we work with certificates. First of all we need to configure the correct time, date, assign a hostname and domain name:
ciscoasa(config)# clock set 12:02:30 17 Nov 2026The clock command will work but using NTP to keep your time synchronized would be better. Let’s configure a hostname:
ciscoasa(config)# hostname ASA1
ASA1(config)#
I’ll call my device “ASA1”. Now we configure a domain name:
ASA1(config)# domain-name NETWORKLESSONS.LOCALThe domain name will be “NETWORKLESSONS.LOCAL”.
In PKI (Public Key Infrastructure) we need to have keys…a public and private key. When we generate an RSA key it will automatically generate these two keys. The public key can be shared with anyone and is used to encrypt messages or to verify signatures. The private key is kept secret and is used to decrypt messages and to sign them. On ASA 9.24(1), the smallest key size you can pick is 2048 bits, modulus 1024 is rejected. Here’s how to generate the keys:
ASA1(config)# crypto key generate rsa label MY_RSA_KEY modulus 2048
Keypair generation process begin. Please wait...
The RSA keypairs were successfully generated.
The key pair is called “MY_RSA_KEY”. You can see them here:
ASA1(config)# show crypto key mypubkey rsa | begin MY_RSA_KEY
 Key name: MY_RSA_KEY
 Usage: General Purpose Key
 Key Size (bits): 2048
 Storage: config
 Key Data:

  30820122 300d0609 2a864886 f70d0101 01050003 82010f00 3082010a 02820101
  00cd5289 88665960 56101720 07e0b4be ebcc8ec3 5a0d29d7 a6aa253d 8d73681f
  3b28aa69 4534cfe8 39e2ec82 8b60b76c 06cde7d8 45ba75c7 8637fcda 70b3dd40
  63da0a05 45bc8380 ca3afbf4 61c6b558 3a04fc35 bb39de6d bff46459 f7cc20c6
  f844b4fa f324dfe1 37377ce2 5854df64 9c8f1566 06c11606 e1caeea1 48e73c95
  e7f4b3d9 97fe33b6 674983fa 2db06c96 d994681e 27a2fd5b 745757eb aa27d147
  d6ae6056 c9d44307 36ffdc43 6146f027 90a1f579 d3de7460 18b3f23c f4d2e6f3
  3aba5edf f54cd664 01038793 db5c92d8 f270a1fe 0bef94b4 cc8b0acb c04f3988
  555298db 0f0e05bc fe456c1e 9ade2e4d dd1dfe36 4088e006 edbf112a 9c403881
  13020301 0001
We now have to create a “trustpoint”. The trustpoint is a container where certificates are stored. This is where we configure parameters like the FQDN, subject name, keypair, etc:
ASA1(config)# crypto ca trustpoint SELF_TRUSTPOINT
ASA1(config-ca-trustpoint)# enrollment self
ASA1(config-ca-trustpoint)# fqdn ASA1.NETWORKLESSONS.LOCAL
ASA1(config-ca-trustpoint)# subject-name CN=ASA1.NETWORKLESSONS.LOCAL
ASA1(config-ca-trustpoint)# keypair MY_RSA_KEY
The trustpoint is called “SELF_TRUSTPOINT” and the enrollment self command means that the ASA will sign its own certificates. The certificate will be assigned to ASA1.NETWORKLESSONS.LOCAL. We will use the RSA keypair that we just generated. We can now enroll the actual certificate. The noconfirm keyword means the ASA doesn’t ask any questions, it doesn’t add its serial number to the subject name and generates the self-signed certificate right away:
ASA1(config)# crypto ca enroll SELF_TRUSTPOINT noconfirm

% The fully-qualified domain name in the certificate will be: ASA1.NETWORKLESSONS.LOCAL
The certificate is now enrolled. We can see it here:
Is there any chance we could get a guide for importing certs from a certificate authority?
Hello Chris
That sounds like a great idea. I suggest you go to the Member Ideas section of the site and post a suggestion to have the topic added.
https://networklessons.com/lesson-ideas
I hope this has been helpful!
Laz
I already try the configuration on the Anyconnect self-signed certificate , but I already get no valid certificate available for authentication. When I write the command sh crypto ssl the result is :
SSL trust-points:
Self-signed (RSA 2048 bits RSA-SHA256) certificate available
Self-signed (EC 256 bits ecdsa-with-SHA256) certificate available
Interface outside: SELF_TRUSTPOINT (RSA 1024 bits RSA-SHA1)
Certificate authentication is not enabled
does this error has to do with Certificate authentication is not enable message?
Hello Alvaro
The “no valid certificate available for authentication” error message usually indicates that the client does not have a valid certificate that can be used for authentication. To resolve this issue, you will need to ensure that the client has a valid certificate that meets the requirements of the server. Some things you can check include the following:
Have you imported the certificate to the user’s computer successfully?
... Continue reading in our forumWhat kind of error message do you receive on the client’s screen?
Are there any other indications on the ASA of the